
In practice
What VMBook implements
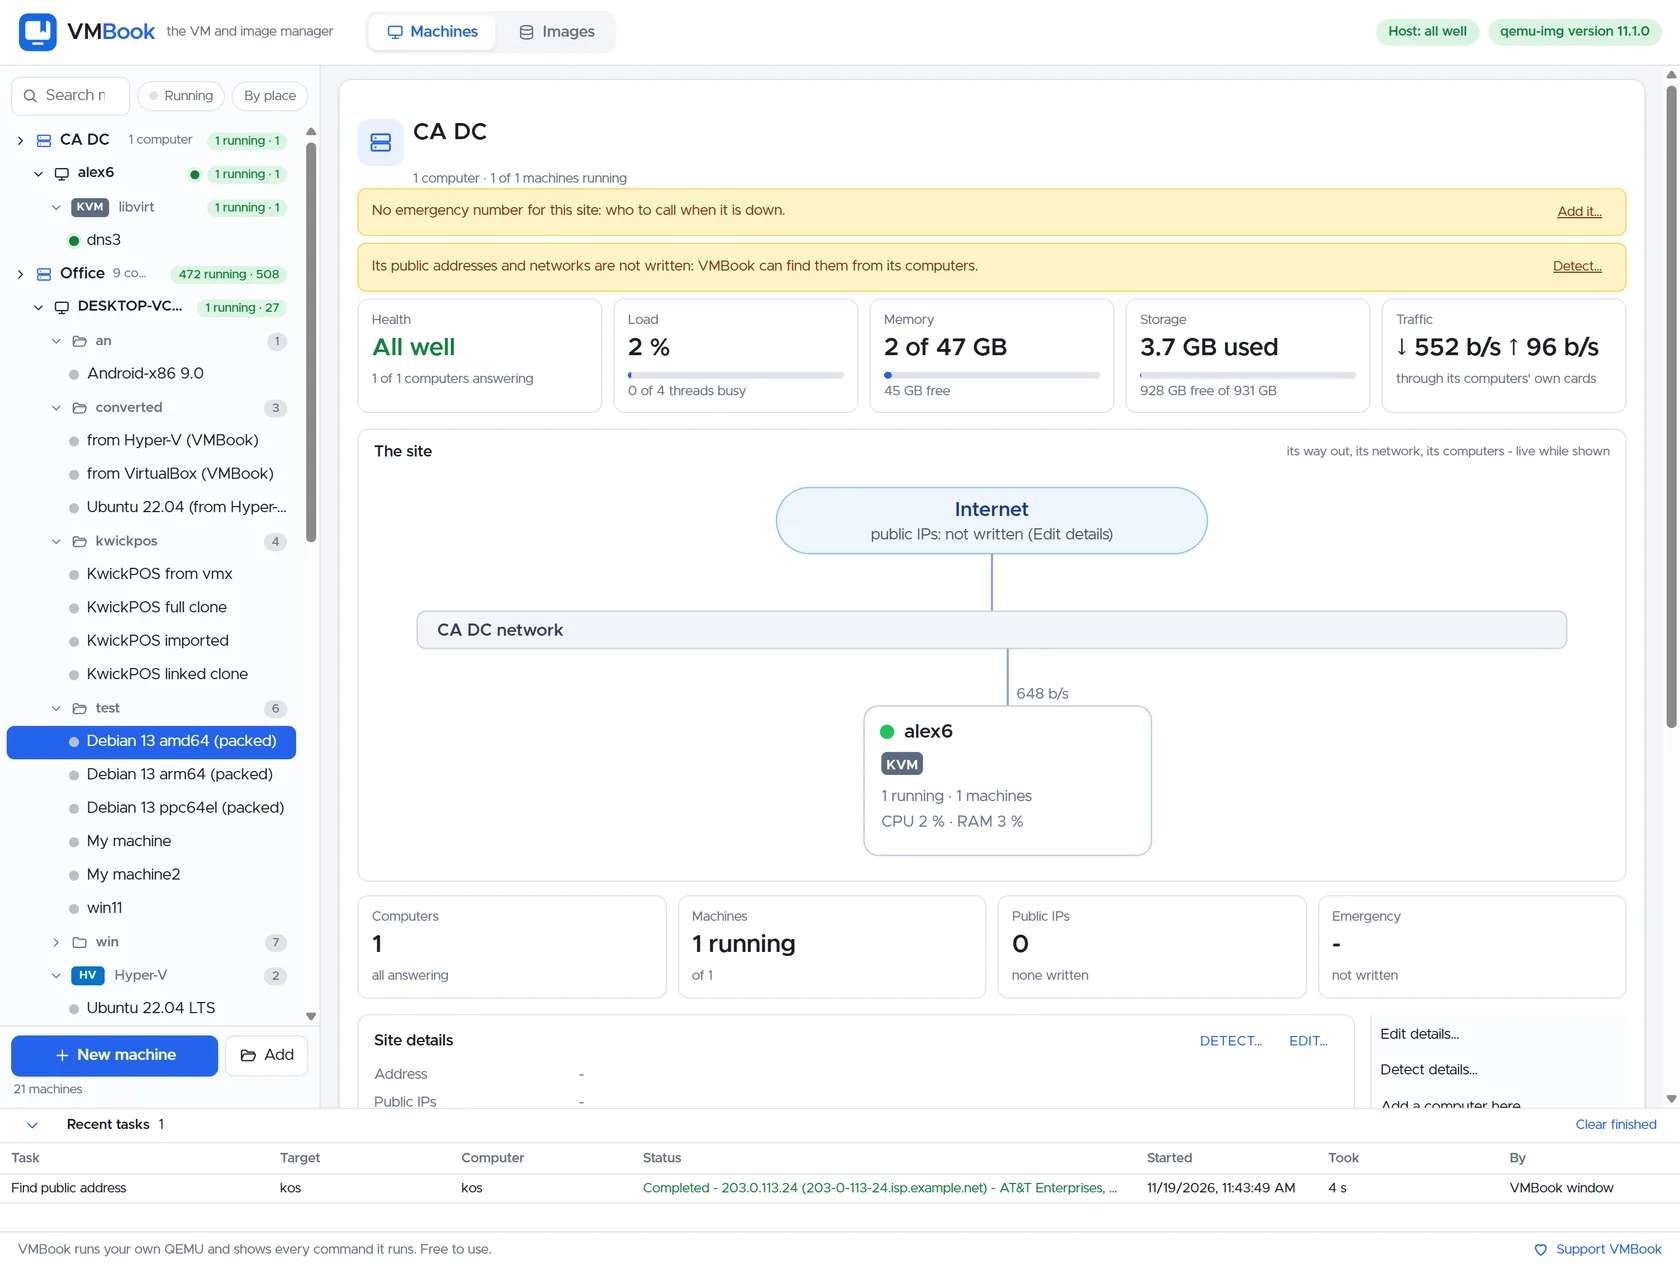
Each agent is a named team principal with its own token, sponsor, scope, rate limit and audit trail; mutation requests require human approval. This capability is kept inspectable: VMBook shows the machine or image state involved and leaves the underlying QEMU operation visible.
A control surface built for bounded agents
VMBook runs an MCP server through its own executable. An agent can inspect capabilities, hosts, usage, BMC state, fleet events, storage, placement, machines, disks, snapshots, backups, devices and selected offline-image data without receiving a general shell.
The agent has its own team identity and token. Its sponsor, grants, site/host/group/machine scope, rate limit, freeze state and activity are visible to administrators.
How a change becomes real
Lifecycle, snapshot and clone tools create an approval request rather than silently changing infrastructure. A human with the same underlying right approves it, VMBook checks state again, runs the defined operation and verifies the outcome. Requests expire, and client request IDs make retries safer.
What MCP does not mean
The current tool set does not expose arbitrary scripts, arbitrary QEMU arguments or team administration. MCP is a structured bridge into VMBook policy; it is not a way around that policy.
Evaluate it
Next step for MCP for AI Virtualization Operations
Review the tested systems for evidence related to MCP for AI Virtualization Operations, then use the free build in an isolated environment with copies of the images involved in your test.